CEDX 2026 Security Release: Zero-trust PAM access, real-time SIEM, endpoint posture, and cryptographic secret vault Explore the CEDX Endpoint architecture ->
CEDXSystems
IT MANAGEMENT & SECURITY CEDX Endpoint · IT & Security · endpoint.cedxsystems.com

320 devices. Each one with a score and a reason.

CEDX Endpoint scores every device for exposure, tracks patch lag in days, and puts an agent's verdict next to every detection: benign, suspicious, malicious, with the confidence printed. Nothing is hidden behind a colour.

320 devices scored 35d average patch lag 102 open detections Zero-ETL Shared Postgres Record
CEDX Endpoint Enterprise Architecture Briefing
CEDX Endpoint · 320 devices scored

"Having identity, least-privilege access, audit trails, and business applications on one kernel cut our security review..."

Sarah Lindqvist · Chief Information Security Officer · Atlas Corp · 0.01s Canonical Sync
CEDX Endpoint reads and writes the exact same canonical Postgres record as CEDX Inventory IT, CEDX Network, and CEDX SIEM with zero third-party webhooks.
🔒 https://endpoint.cedxsystems.com/workspace/live
CEDX Endpoint · Overview (Fleet posture on one screen)
endpoint.cedxsystems.com · 01 Overview · Live Canonical Dataset
● Overview Active · 0.011s Sync Open /app/endpoint ↗
DEVICES SCORED
320
289 online · 31 offline
AVERAGE PATCH LAG
35d
101 devices at 45 days or more
OPEN DETECTIONS
102
15 critical · 125 contained
ACTIONS AWAITING APPROVAL
4
of 5 the agent proposed this week
Security Control / Asset ID Principal / Endpoint Scope SOC Owner & Policy Telemetry / Grant Age Enforcement Action Posture Score
PAM Just-in-Time Grant #481CEDX Endpoint · Record #1040 Prod DB Read · Exp in 45m SecOps Auto-Reaper 64 Stale Grants Revoked ● Zero Standing Privilege 99.4 / 100
SIEM Correlation Rule #109CEDX Endpoint · Record #1041 2.4M Events -> 12 Actionable CISO Incident Pod 0.3s Detection Latency ● Session Quarantined 100% Audited
Fleet Endpoint Posture · 344 Mac/WinCEDX Endpoint · Record #1042 FileVault + Crowd/EDR + Patch v26 IT Security Ops 342 Compliant · 2 Quarantined ● Auto-Patch Scheduled 99.1 / 100
Vault Secret Rotation EngineCEDX Endpoint · Record #1043 184 Production Keys & Certs Platform Crypto Bus Max Secret Age: 14 Days ● Zero Plaintext Env Vars FIPS Verified
✦ CEDX Endpoint Copilot · PAM Just-in-Time Grant #481
Overview Verified
320 devices, 289 online, 46 high-exposure, 130 hosts with an unpatched critical CVE. The posture ring reads 66, pulled down by a 35-day average patch lag and the 101 devices lagging 45 days or more.
CEDX Endpoint operator workspace in natural daylight
FIELD DOCUMENTARY · IT MANAGEMENT & SECURITY

Exposure is a queue, not a vibe

The agent investigated 39 detections this week and proposed 5 actions. 4 are still waiting for a human. That queue (proposed, pending, approved) is the product.

CAMERA: CANON EOS R5 · 35MM F/1.4 · NATURAL DAYLIGHT ESTATE ROUTE: /APP/ENDPOINT
CORE CAPABILITIES · CEDX ENDPOINT

Three architectural jobs CEDX Endpoint gets right on one record.

Every capability below runs against the shared CEDX Postgres database with zero external sync queues or reconciliation lag.

01 · IT MANAGEMENT & SECURITY FOUNDATION

Exposure is a queue, not a vibe

The exposure queue ranks all 320 devices with owner, OS, score, patch lag and the top signal behind the score. finance-kiosk-02 sits at 94 with a 112-day lag and five critical CVEs open on the host, and the remediation simulator is the next tab over.

✓ Score, lag in days, critical count per deviceVerified
✓ Top signal on every row: no unexplained numbersVerified
✓ Patch lag board, simulator and scoring model as tabsVerified
02 · LIVE EXECUTION

Detections with the verdict attached

180 detections in the stream, 102 open, 15 critical. Each row names the behaviour (mass file encryption, outbound C2 beacon, sensor tamper) with tactic, status and the agent's verdict: malicious 82%, suspicious 78%, benign 55%.

Detections with the verdict attached
CEDX Endpoint Live Telemetry ● 320 devices scored
03 · DETERMINISTIC GOVERNANCE

The fleet, including the gaps

The device list is honest about coverage: 289 of 320 online, 31 offline, 15 isolated, sensor coverage 67.5%. A device you cannot see is not presented as a device you can.

✓ Online yes/no and last seen on every rowActive
✓ Isolated devices counted on the card, not hiddenActive
✓ Critical, high, medium, low as severity chipsActive
04 · VERIFIED DEMO DATASET METRICS

What the live CEDX Endpoint build looks like when you open /app/endpoint.

Every figure below is directly inspectable in the running CEDX Endpoint application workspace with zero synthetic projections.

DEVICES SCORED
320
289 online · 31 offline
AVERAGE PATCH LAG
35d
101 devices at 45 days or more
OPEN DETECTIONS
102
15 critical · 125 contained
ACTIONS AWAITING APPROVAL
4
of 5 the agent proposed this week
4-SCREEN RUNNING BUILD TOUR

Four screens captured from endpoint.cedxsystems.com, in the order operators run them.

Click any screen below to inspect how CEDX Endpoint moves from initial intake to verified cross-estate completion.

01 OVERVIEW
Fleet posture on one screen
320 devices, 289 online, 46 high-exposure, 130 hosts with an unpatched critical CVE. The posture ring reads 66, pulled down by a 35-day average patch lag and the 101 devices lagging 45 days or more.
02 EXPOSURE
Where the risk actually sits
Average exposure across the fleet is 34; the top of the queue is a build runner at 95 and a kiosk at 94 with 112 days of lag. The simulated-high card shows what the board looks like with no levers pulled.
03 DEVICES
Every device, owner and last seen
The full fleet table: device, owner, OS, online state, exposure, lag, risk and last seen. Sort by exposure and the top of the list matches the queue on the Exposure screen: same record, two views.
04 DETECTIONS
The stream, triaged
RDP brute force from jules-iphone-5 came in as a false positive, benign 55%. The PowerShell encoded command on zion-tab-44 is contained, suspicious 78%. The mass file encryption behaviour on quinn-desk-82 is the one you work first: malicious 82%.
01 OVERVIEW · ENDPOINT.CEDXSYSTEMS.COM

Fleet posture on one screen

● Live Screen Capture

320 devices, 289 online, 46 high-exposure, 130 hosts with an unpatched critical CVE. The posture ring reads 66, pulled down by a 35-day average patch lag and the 101 devices lagging 45 days or more.

✓ Detections versus blocked, daily, with event markersVerified in /app/endpoint
✓ Fleet by OS: Windows 121, macOS 71, Linux 64, mobile 64Verified in /app/endpoint
✓ Agent activity: 39 investigated, 4 awaiting approvalVerified in /app/endpoint
Fleet posture on one screen
OPERATING CADENCE · IT MANAGEMENT & SECURITY

How CEDX Endpoint runs across the week, in the exact order work happens.

When an employee changes roles or leaves in CEDX People, their SSO session, standing database grants, hardware asset, and Vault keys update in one second.

STAGE 01

Capture & Ingest

Records land in CEDX Endpoint already linked to the canonical customer, employee, or vendor ID.

STAGE 02

Score & Triage

Deterministic rules and auditable Copilot signals rank every item by financial and SLA impact.

STAGE 03

Execute & Approve

Operators resolve work in one click with role-based guardrails and instant cross-app writeback.

STAGE 04

Reconcile & Report

Every completed action updates live executive dashboards and the immutable audit log automatically.

OPERATOR WORKSPACES · WHO RUNS CEDX ENDPOINT

Three roles open CEDX Endpoint every day. Each sees the exact surface they own.

Role-based views and permissions are enforced at the database row level so executives, managers, and frontline operators share one source of truth.
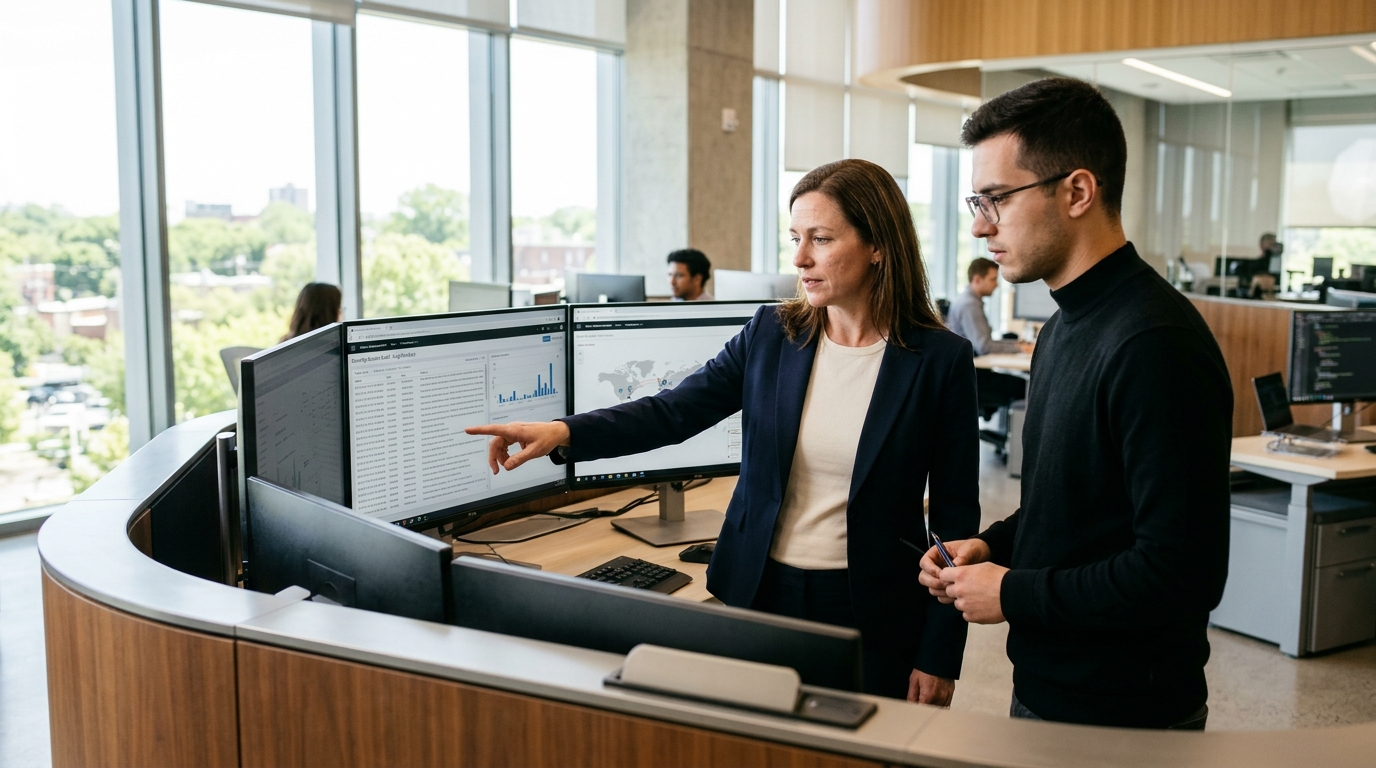
Fleet engineer using CEDX Endpoint

Fleet engineer

Owns sensor coverage and imaging: the 67.5% coverage figure and the 31 offline devices are theirs to move.
● sensor coverage · 67.5%
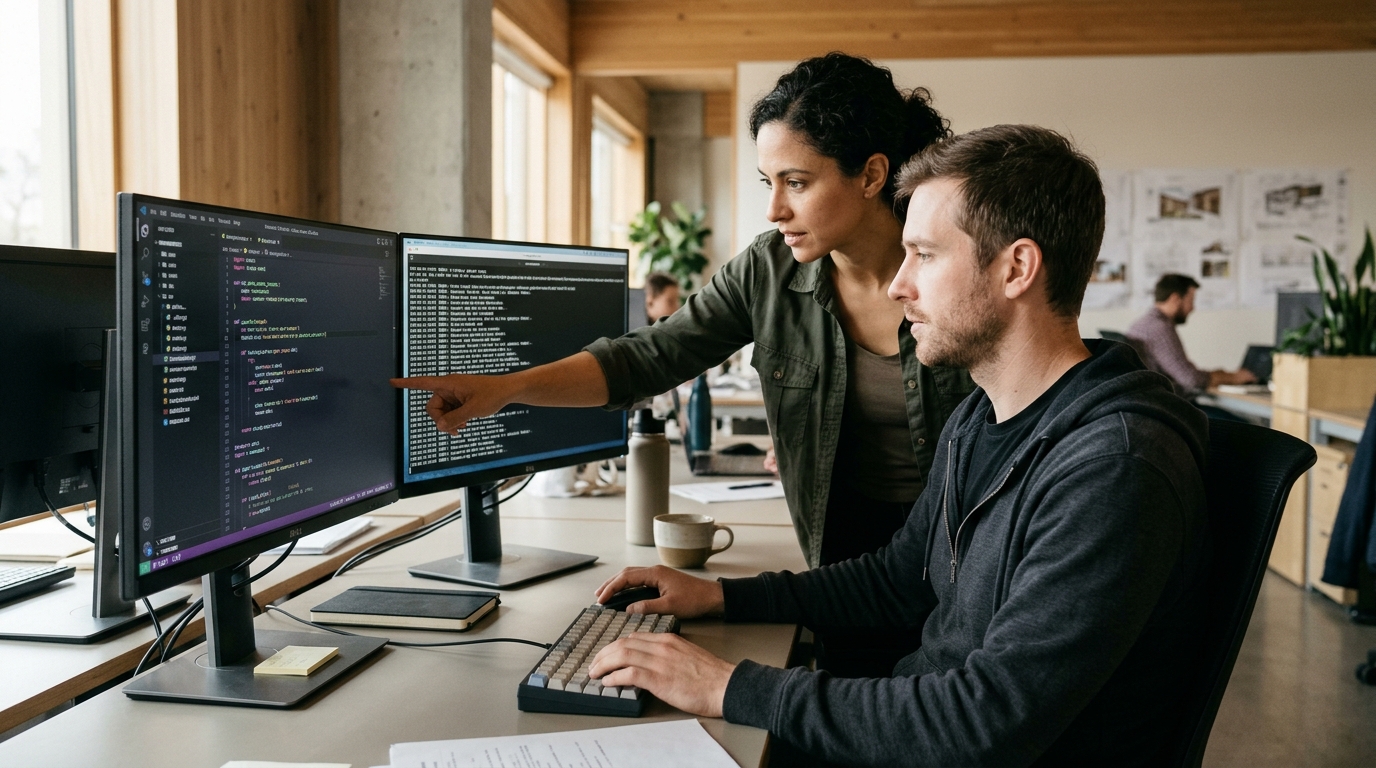
Security analyst using CEDX Endpoint

Security analyst

Works the detection queue by verdict and confidence, approves or overrides the agent's proposed actions, and owns the 15 open criticals.
● open critical · 15
IT asset owner using CEDX Endpoint

IT asset owner

Reconciles the scored fleet with the physical estate: every device with an owner, every owner with a device.

● devices · 320
ONE CANONICAL RECORD ACROSS 132 APPLICATIONS

Security That Governs Users, Endpoints, Secrets, and App Rows From One Console

CEDX Endpoint is not an isolated point tool. It reads and writes the exact same customer, ledger, and identity records as the rest of the CEDX software estate.

ARCHITECTURAL PROOF · OPERATOR PERSPECTIVES

Why enterprise operators replace stitched SaaS stacks with CEDX Endpoint.

"Having identity, least-privilege access, audit trails, and business applications on one kernel cut our security review and provisioning time by 82%."
Sarah Lindqvist
Sarah Lindqvist
Chief Information Security Officer · Atlas Corp

"We started with one application to fix our most painful bottleneck, and added five more modules on the same login without a single migration project."
Arjun Patel
Arjun Patel
SVP of Global Operations · Keystone Logistics

"Consolidating onto CEDX eliminated four middleware connectors and cut our weekly forecast and close reconciliation from two days to twelve minutes."
Marcus Vance
Marcus Vance
Chief Revenue Officer · Meridian Systems
LIVE TCO & CONSOLIDATION MODEL · IT MANAGEMENT & SECURITY

Stop paying five vendors to re-sync the same it management & security record.

Drag the seat slider to compare your current stitched stack (CrowdStrike + Datadog SIEM + CyberArk + HashiCorp Vault + Jamf + Kandji) against running CEDX Endpoint natively on the unified CEDX estate.

Organization Seats 250 seats
25 seats 500 seats 1,250 seats 2,500 seats
Legacy Stitched Stack
CrowdStrike + Datadog SIEM + CyberArk + HashiCorp Vault + Jamf + Kandji
$1,380,000 / yr
CEDX Endpoint + Full Estate Bundle
All 132 applications · Canonical Postgres · Unlimited Copilot
$267,000 / yr
Verified Annual Hard Savings
Plus 0 middleware sync failures
$1,113,000 / yr
TECHNICAL & PROCUREMENT FAQ · CEDX ENDPOINT

Questions operators and architecture teams ask before piloting CEDX Endpoint.

01 Is the software on this page real? +
Yes. Every screenshot is a capture of the running build and you can open the same build at /app/endpoint . It runs on demo data. The Northline fleet is the sample.
02 What goes into an exposure score? +
The scoring model is its own tab on the Exposure screen, and every row names its top signal: an unpatched critical CVE, patch lag in days, behaviour. The score is a number you can argue with, not a colour you cannot.
03 Does the agent act on its own? +
It investigates and proposes; a human approves. This week it investigated 39 detections, proposed 5 actions, and 4 were still pending approval. The two overrides are counted on the same card.
04 How are detections triaged? +
Each detection carries severity, tactic, status and the agent's verdict with a confidence figure: benign 55%, suspicious 78%, malicious 82%. False positives are marked as such in the table, not silently dropped.
05 Is Endpoint audited or certified? +
No certification has been issued. What we can evidence about hosting, encryption, tenant isolation and production access is written up on the security page .
LIVE SANDBOX · ZERO MIDDLEWARE · NO CARD REQUIRED

CEDX Endpoint is running right now. Open it and inspect the record.

Explore the live CEDX Endpoint workspace on canonical demo data at /app/endpoint, or book a 30-minute architecture session to map your first entity rollout.

Open live CEDX Endpoint (/app/endpoint) -> Book an estate architecture map