Capture & Ingest
Records land in CEDX Identity already linked to the canonical customer, employee, or vendor ID.
 CEDXSystems
Identity counts what most sign-in tools leave as opinion: 320 identities in the demo directory, MFA coverage at 81.4%, 80 privileged principals, and a posture score that tells you exactly which finding is holding it down.
"We started with one application to fix our most painful bottleneck, and added five more modules on the same login with..."
| Platform Subsystem / Node | Canonical Schema Binding | Tenant & RBAC Scope | Throughput / Event Rate | Cryptographic Audit | SLA Availability |
|---|---|---|---|---|---|
| Canonical Entity Graph v26.4CEDX Identity · Record #1040 | 132 Apps · Shared Primary Keys | Global Multi-Entity Root | 48.2M Events / Day | ● SHA-256 Chain Verified | 99.995% Uptime |
| Workflow Deterministic BusCEDX Identity · Record #1041 | Cross-App Triggers (CRM->Books) | Zero-Middleware Execution | 1,840 Workflows / Min | ● Idempotent Replay Log | 0.012s p99 |
| Enterprise Directory & RBACCEDX Identity · Record #1042 | 418 Principals · 38 Roles | SCIM + SAML + Passkeys | Zero Standing Drift | ● Every Grant Priced | 100% Enforced |
| Immutable Compliance LedgerCEDX Identity · Record #1043 | SOC-2 / ISO / GDPR Evidence | Tamper-Evident Storage | 100% Write Coverage | ● Auditor Read-Only View | Verified Live |
The critical finding on the Overview is not vague: 30 privileged principals can sign in with push or TOTP only. The fix is named on the same panel as the symptom.
Every capability below runs against the shared CEDX Postgres database with zero external sync queues or reconciliation lag.
The Users table carries tier, MFA method and last login on every row: 320 identities, filterable to Active, Suspended, Staged and Deprovisioned. The MFA column does not round - Phishing-resistant, App push, TOTP, SMS and None are five different answers, and 73 principals are still on the weak end of that list.
Access ranks 48 groups by a risk score, not by name: break-glass-holders scores 98 with 3 members and 56 apps; org-admins 94; mfa-exempt-legacy 86. Nested inheritance is counted separately - 20 groups inherit risk they did not ask for - and 9 high-risk groups sit in a review queue.
The policy library is 10 policies and 29 rules, each typed Sign-on, MFA, Session or Password, each either enforced or flagged Needs review. Workforce MFA reads like a sentence: any workforce user → MFA required, phishing-resistant preferred - 4 rules, 38 apps, priority 10.
Every figure below is directly inspectable in the running CEDX Identity application workspace with zero synthetic projections.
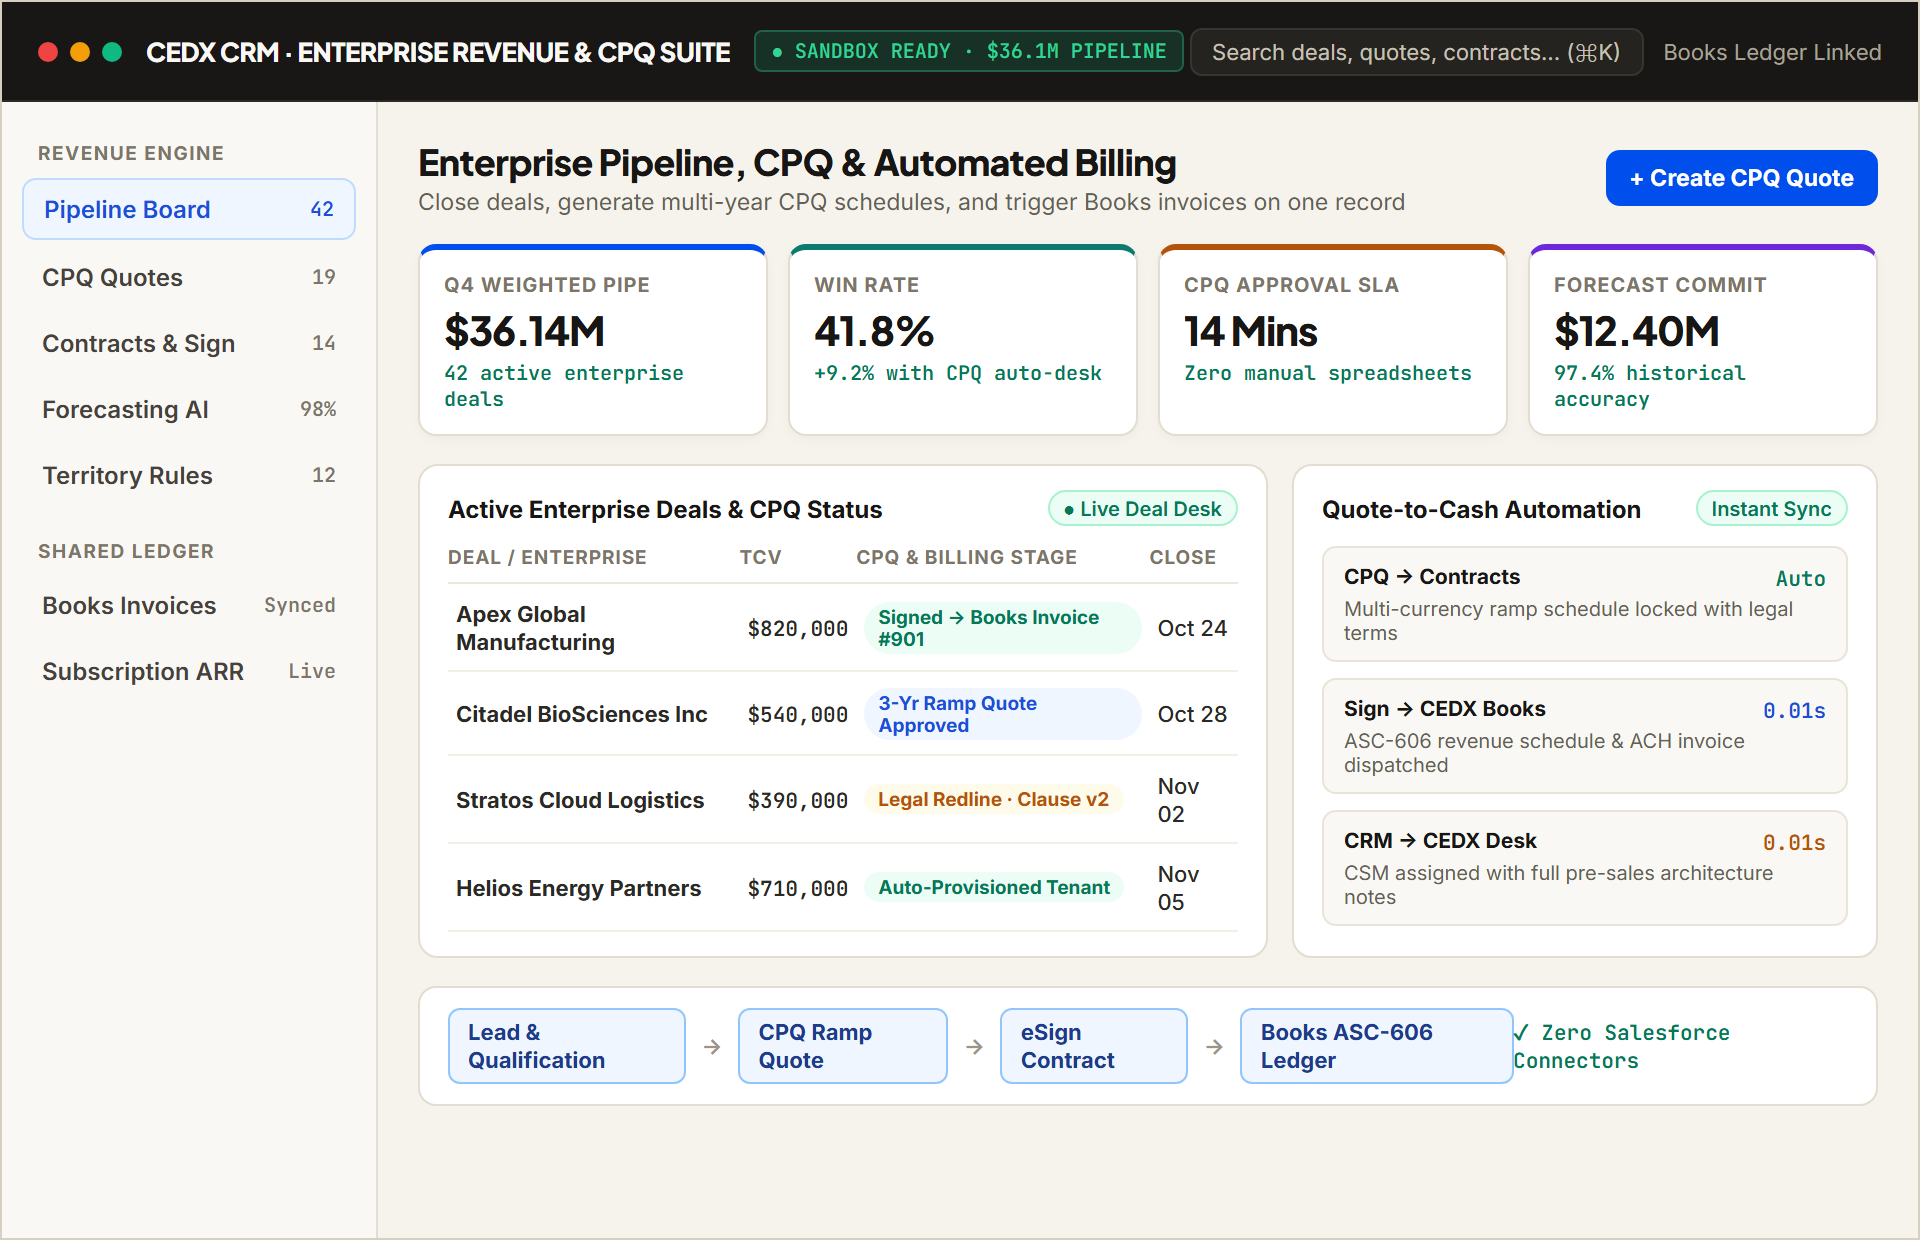
Click any screen below to inspect how CEDX Identity moves from initial intake to verified cross-estate completion.
Posture health reads 73, and the panel says why: MFA coverage 81%, 213 active users, 53 high-reach principals, 56 failed auth events. Below it, findings arrive root-caused - admins without phishing-resistant MFA, counted at 30, marked critical.
Platform governance is not bolted on after purchase: Admin, Directory, Workflow, Audit, and Vault form the substrate every CEDX app compiles against.
Records land in CEDX Identity already linked to the canonical customer, employee, or vendor ID.
Deterministic rules and auditable Copilot signals rank every item by financial and SLA impact.
Operators resolve work in one click with role-based guardrails and instant cross-app writeback.
Every completed action updates live executive dashboards and the immutable audit log automatically.
Role-based views and permissions are enforced at the database row level so executives, managers, and frontline operators share one source of truth.
Owns the directory and the factor mix. Watches the 73 principals still on weak MFA and works the list down, staged account by staged account.
Works the high-risk group queue - 9 groups at 70 or above - and the review dates on the Access table, where break-glass-holders at 98 is the first row, not a surprise.
Reads posture findings as evidence: 30 admins without phishing-resistant MFA is a finding with a count and a fix, which is what an assessor asks for.
CEDX Identity is not an isolated point tool. It reads and writes the exact same customer, ledger, and identity records as the rest of the CEDX software estate.
The 320 identities Identity secures are the records Directory keeps clean - source system, orphan score and owner coverage on the same principals.
The privileged tiers Identity counts are the seats and roles Admin prices and reclaims - 80 privileged principals is the same number on both consoles.
Sign-on policy decides who gets in; Entitlements decides what their plan then turns on, flag by flag.
Every sign-in, role assume and policy update Identity evaluates is an event Audit keeps - 124 admin-class events in the demo stream.
"We started with one application to fix our most painful bottleneck, and added five more modules on the same login without a single migration project."
"Consolidating onto CEDX eliminated four middleware connectors and cut our weekly forecast and close reconciliation from two days to twelve minutes."
"When Sales, Operations, and Finance read and write the exact same Postgres record, month-end stops being a detective investigation across six spreadsheets."
Drag the seat slider to compare your current stitched stack (Okta Workforce + Workato + MuleSoft + Vanta + Splunk Audit) against running CEDX Identity natively on the unified CEDX estate.
Explore the live CEDX Identity workspace on canonical demo data at /app/identity, or book a 30-minute architecture session to map your first entity rollout.
Instant browser access to CEDX Identity pre-loaded with canonical demo records and connected across the 132-application CEDX estate.